Perspectivas y recursos sobre riesgo humano
Análisis detallados, datos y recursos prácticos para equipos centrados en reducir el riesgo provocado por el comportamiento.
5 min de lectura
usecure lanza uHealth, el producto que define el Human Risk Intelligence (HRI)
usecure lanza uHealth y acerca el Human Risk Intelligence a los MSPs y a los equipos de TI conectando señales de identidad, concienciación, higiene y acceso para revelar y reducir el riesgo cibernético humano.
Kerryn Zendera

5 min de lectura
8 best human risk reporting platforms for MSPs
Compare 8 human risk reporting platforms for MSPs. Explore risk scoring, client reporting, integrations and features that go beyond training completion.
Kerryn Zendera
5 min de lectura
8 best security policy management platforms for MSPs and SMBs
Compare 8 security policy management platforms for MSPs and SMBs. Explore policy templates, acknowledgments, reporting and Human Risk Intelligence.
Kerryn Zendera
5 min de lectura
7 best dark web monitoring tools for MSPs in 2026
Compare 7 dark web monitoring tools for MSPs in 2026. Explore usecure, Kaseya, Guardz and more across features, reporting, MSP fit and key tradeoffs.
Kerryn Zendera
5 min de lectura
What Is PHI? A Guide to Protected Health Information, HIPAA Identifiers, and Key Exclusions
What counts as protected health information (PHI), and where do its boundaries lie? This blog explains the two-part test for identifying PHI, the 18 HIPAA identifiers, and common and overlooked examples, from medical records to appointment reminders and website tracking data. It also clarifies what is not PHI, distinguishes PHI from electronic PHI (ePHI), and explores how everyday workforce decisions can expose patient information. Learn why recognizing PHI and understanding human risk are both essential to protecting patient privacy.
Yu Ling Lok
5 min de lectura
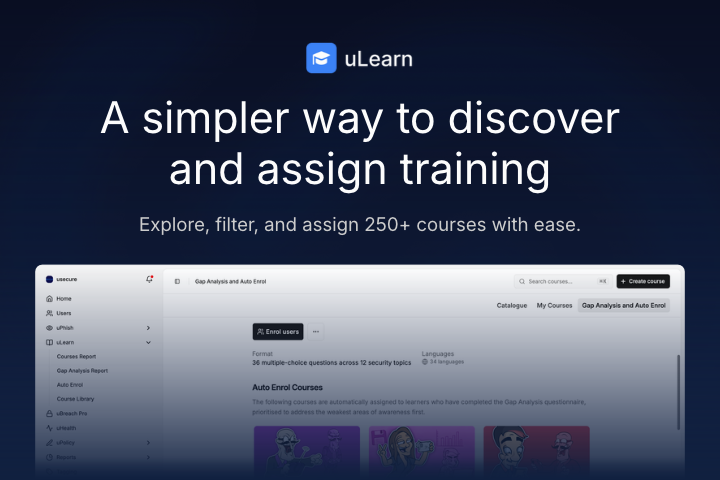
Meet the new uLearn Course Library: find the right training, faster
We've redesigned the uLearn Course Library to help you discover relevant training and get learners enrolled in fewer steps.
Kerryn Zendera

5 min de lectura
HIPAA Training Requirements (2026): Who Needs It, How Often, and What to Cover
HIPAA training requirements apply to every workforce member at a covered entity or business associate. Training is required at onboarding, after material policy changes, and through an ongoing security awareness program, with records kept for six years. HIPAA annual training is not written into the current rule, but OCR settlements and the proposed Security Rule treat it as the minimum. In 2026, the organizations best protected are those that pair role-based training with Human Risk Intelligence to see which humans carry the most risk.
Yu Ling Lok
5 min de lectura
What 2026 cybersecurity data reveals about employee exposure
usecure's Human Risk and Compliance Outlook Report reveal why training, phishing results, and identity controls need to be connected to understand real human risk.
Kerryn Zendera
5 min de lectura
Novedades de producto de octubre de 2026: nueva formación, campañas y análisis para octubre
Tu Product Pulse de octubre: recursos para el Cybersecurity Awareness Month, formación en concienciación en seguridad nueva y actualizada, enablement para partners y análisis de amenazas.
Kerryn Zendera